

Let’s say the scenario that doomsayers in Silicon Valley fear comes to pass, and AI kills us all. Scratch that. Say it kills some of us versus all of us, or takes down the electrical grid for a week. I think we can confidently predict that two groups of people will be busy in the days that follow:
1. Lawyers, who per strange bedfellows Lina Khan and Mark Zuckerberg will have a lot of product liability suits to file, and...
2. Insurers, who will have an equally large volume of claims to process.
Or maybe just deny. It’s hard to say for sure, because the degree to which insurance policies generally and cyberinsurance policies specifically cover AI-related harms is still mostly undefined.
Kind of the way coverage for security-related harms was undefined in the insurance industry’s so-called “silent cyber” era. That was back when growing masses of breach victims were filing claims against business or property policies that said nothing one way or the other about breaches. The inevitable results included overworked claims processors, denied claims, and unhappy customers. Cyberinsurance as we know it was invented largely in response to that dynamic.
These days, we find ourselves in a “silent AI” era in which most policies across multiple categories either say nothing about losses involving AI or say something you’d rather not hear.
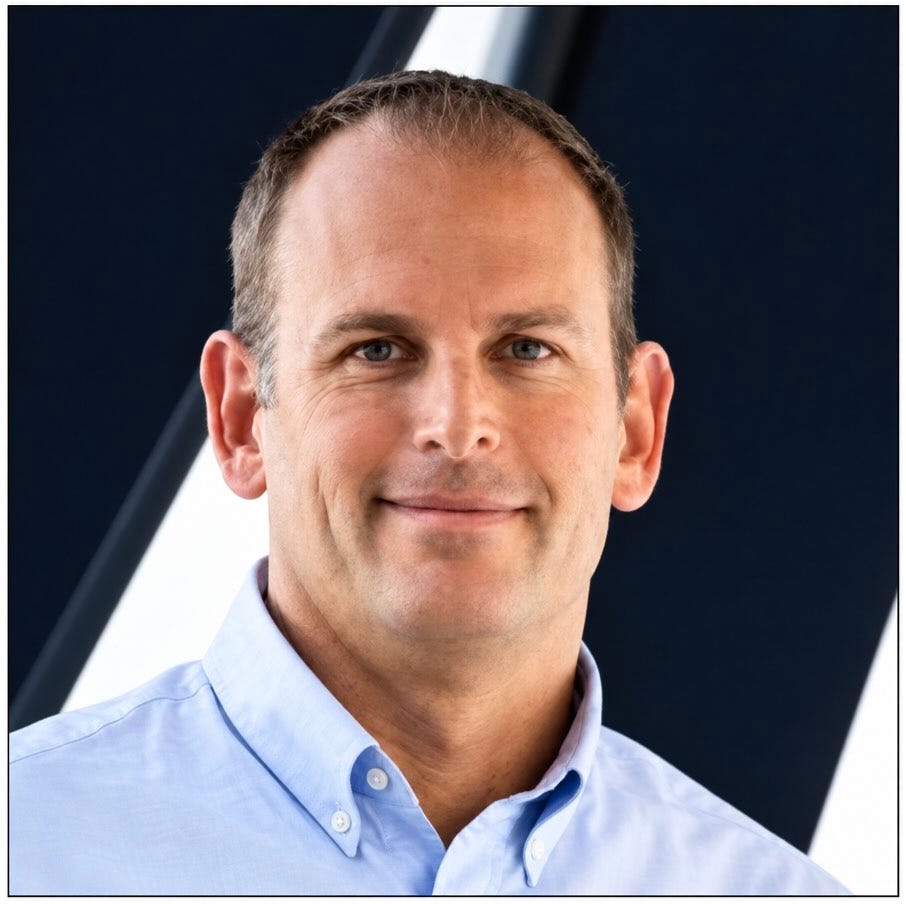
“All the big shops, the big boys, the AIGs, the Chubbs, the Travelers, the Nationwides, you name it, are saying we’re going to exclude any form of AI in general liability, director and officer, and cyber [insurance], because they have no idea how to wrap their head around it let alone price it,” says Edouard von Herberstein (pictured), CEO of SPECTRA, a cyber risk management vendor for MSPs.
The situation’s actually a little more nuanced, according to Michael Phillips, head of global cyber portfolio underwriting at Coalition. Many insurers have filed with state governments (successfully 80% of the time to date) for the right to add AI-related exclusions to their policies, but not all of them have done so, and those that have generally aren’t excluding cyberinsurance coverage for victims of a breach committed by an agent or AI-equipped threat actor.
“If you are buying a specialty cyber product, you typically don’t have to fear that your cyber underwriter is adding an exclusion for AI-driven cyber security attacks,” Phillips says.
Especially, he adds, if your underwriter is Coalition. “In 2024, we revised all of our cyber and tech policies to include what we called affirmative AI language” specifying coverage for AI-powered or executed attacks. Last year, the company introduced a policy enhancement that protects businesses from the effects of deepfake imposters damaging their client relationships and reputation. Liability coverage for incidents in which AI is guilty of copyright infringement, defamation, slander, and the like followed the week before last.
Other insurers now have affirmative language about AI in their cyber policies too, including Beazley as of last week. But most of it addresses AI use by attackers. According to Phillips, carriers have begun explicitly excluding coverage for incidents in which a company’s own AI does something it shouldn’t, like break into—oh, I don’t know—Hugging Face.
Those still silent on the topic may not be there when you need them either, notes Frank Merino, CTO of Forthright Technology Partners, an IT, security, and compliance solution provider based in Weston, Fla. What happens if a shadow AI user in your office inadvertently deletes your website or leaks critical IP? From an insurance carrier’s perspective, Merino notes, that’s not force majeure.
“You told it to do something and it did it,” he says. “If it puts you out of business or materially impacts your ability to conduct business, whose fault is that?”
Right now, that’s a hypothetical danger for Forthright clients, few of whom have filed an AI-related claim or had one denied. But Merino’s convinced it’ll be all too real eventually as more and more businesses vibe code apps and deploy autonomous AI.
“I really think that this issue is going to come,” Merino says.
And remember, we’re talking about it coming to people with cyberinsurance policies. Yet roughly a third of businesses with 100 to 2,000 employees don’t have such coverage, according to insurer QBE. Those companies are presumably relying on other forms of coverage that are either dangerously silent on AI or ripe prospects for AI exclusions.
“If you’re only buying an extension to a package policy or a more comprehensive business owner’s policy that’s protecting you from fire, wind harm, etc., then you do have to worry about that,” Phillips warns.
Filling the AI risk gap
SPECTRA sees AI exclusions coming too and is doing something about it now. Its existing products help MSPs get better coverage and lower rates for clients by certifying their use of security best practices. In the hope of eventually providing similar rewards for embracing AI security best practices, the company recently began piloting an AI risk framework composed of 20 deployment controls.
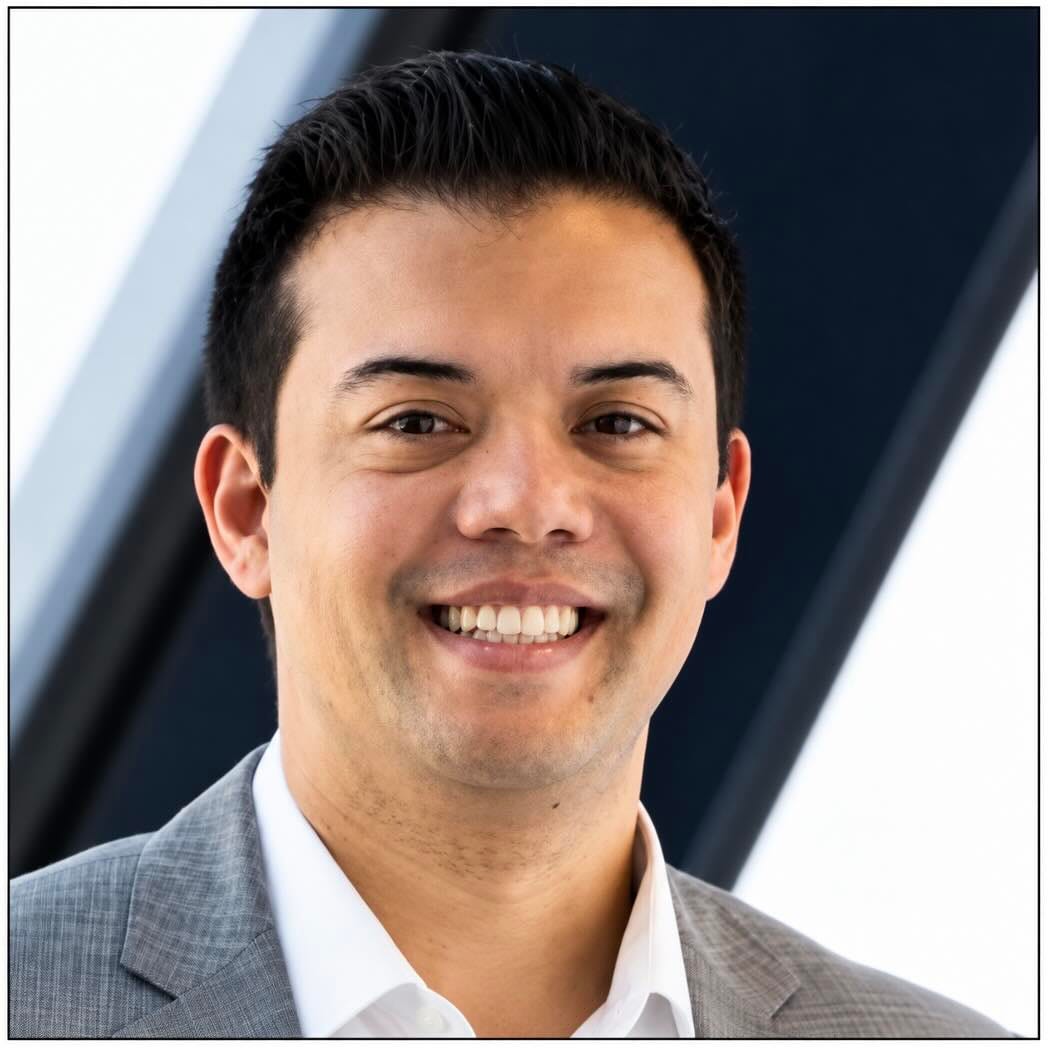
“There isn’t really an industry-recognized framework for AI technologies,” says Eric Altamura (pictured), SPECTRA’s COO. “We figured there’s a role for us to play that’s kind of true to what SPECTRA already does for our partners, which is identify agreed upon security standards, evidence the deployment of those controls, and then structure the data in a way that can be consumed by the underwriter.”
Von Herberstein hopes those underwriters respond appropriately. “We are very actively working with Lloyd’s of London and in the U.S. to unlock what currently doesn’t really exist, which is broad and deep affirmative AI coverage for businesses big and small,” he says.
Forthright is an early adopter of the framework, which it sees less as a potential way to add revenue than as a way to retain the trust of its clients. “I don’t make a dollar,” Merino says. “There’s zero benefit for me in this, other than that you’re working with me and I’m telling you this is the right path.”
According to Altamura, SPECTRA expects to modify the framework regularly. “We built it in a way that I think is meant to be flexible and adaptable because at the rate that things change and just the number of updates that Anthropic pushes out to Claude on a daily basis, we need something that can be refined over time.”
Phillips views change as the only constant in AI cyberinsurance too. Coalition modifies its policies in response to new models and threats every quarter, and its pricing even more often.
“We’re updating that very regularly because it’s so new that every little incident is material to our data set,” he says.
And there are a lot of new incidents in everyone’s future.
New on MSP Chat: Getting stronger by getting help
There’s no shortage of resources out there for MSPs looking to find leads, win deals, motivate technicians, and add services. Why has there never been a resource for MSPs coping with the unrelenting emotional and mental pressure of being an MSP until MSP Well (which I wrote about earlier this year) created it? We get into that and more with two of the community’s leaders on the latest episode of MSP Chat, the podcast I co-host, and get into similarly important topics every week right here.
How many tokens is too many?
Not long ago, a young company named Retool configured an agent to schedule out-of-office notifications for employees automatically. That’s exactly the kind of tedious, low-value task agents are made to automate and would have been a nice little AI success story if not for the fact that the agent in question was consuming $10,000 worth of tokens a day without anyone noticing.
Retool’s not the only recipient of an unexpectedly enormous token bill this year, if it’s any consolation to them. Uber famously blew its entire 2026 AI budget in four months while another company understandably reluctant to identify itself spent half a billion dollars on AI in a single month earlier this year.
That was back in the “tokenmaxxing” era though, when at least some businesses briefly decided that burning more tokens faster is always, inherently better. These days, the tide has shifted toward tracking, controlling, and optimizing token consumption. The memory of those earlier headlines lingers nonetheless.
“Those stories created anxiety,” says Shane Cronin (pictured), head of FinOps & ITAM services at tech solutions giant SHI. “Then that anxiety accelerated the need for a lot of people to come together and try and find a way to solve for this more broadly.”
Come together they did too last month, when 44 organizations ranging from Accenture and SHI to ServiceNow and SAP formed the Tokenomics Foundation, an offshoot of the non-profit Linux Foundation dedicated to “establishing open industry standards, benchmarks and best practices for the economics of AI.”
And not a moment too soon either as organizations find themselves using AI more but struggling to measure, let alone manage, the spending associated with that usage. Indeed, nearly 47% of businesses surveyed by Futurum came in over budget on AI in the first half of this year even as per-token prices are plummeting. Just 5.6% came in below.
If the Tokenomics Foundation’s mission was simply helping decision-makers get a grip on all that spending, it would be doing good work. What it’s really up to, though, is even harder, more interesting, and more needed. Businesses, the foundation believes, can’t right-size their investment in AI without first understanding their return on that investment, and they can’t determine that return without first determining both what they’re spending on AI and how much value that spending is getting them. That last part in particular is a real problem for most companies, Cronin observes.
“They’re trying to calculate this and they’re trying to find a defensible position to the CFO, but almost nobody is really meeting that quality threshold,” he says.
The foundation, whose work on the topic is still very much in progress, aims to help close that gap by developing more rigorous techniques for measuring AI’s cost and value. On the cost side, that involves looking past token spend alone to what the foundation calls TCA, as in total cost of AI.
“We have to think a bit more broadly about the real cost of AI as being everything that actually goes into energy, capital, silicon, data centers, software licensing, and the labor that’s required to actually build and review and supervise AI,” Cronin says.
The value side of the equation is even more thorough, encompassing ten categories across three groups. “Direct dollar wins” assesses things like revenue added or costs reduced. Labor weighs capacity gains and workflows either augmented or fully automated. And “reported outcomes” quantifies product quality, speed to market, risk reduction (think IT outages or compliance issues avoided), and new capabilities, as in the newly acquired ability to accomplish things you couldn’t do before AI made them possible.
It’s a complicated formula, but an immensely valuable one if it holds up for MSPs evaluating value-based AI pricing schemes that businesses will embrace only if the value they’re paying for is precisely defined and demonstrated.
Learning how to achieve that precision will take time, but MSPs who complete the journey will have not only a powerful tool for selling high-margin AI services but a new service offering potentially as well. Businesses desperately want help justifying all of their AI bills, not just the one their IT provider sends them every month.
“If we can master that, that’s a huge opportunity for MSPs,” Cronin says.
Outcomes are golden in AI
A lot of people in a lot of places have told you that data is gold in AI over the last few years, and I’ve been among them.
We’ve all been wrong.
Well, not wrong exactly. You do need clean data to get good output from AI, and having a lot of it usually beats having a little. It’s just that calling data AI gold distracts attention from what makes AI monetizable for frontier labs, software makers, and MSPs alike. Businesses have plenty of data and don’t want more, observes Mike Sanders (pictured), a former C-suite executive at Kaseya who’s now CEO of Upshop. “What they want is for that data to provide something that can be executed at whatever level it needs to be executed to offset a bad outcome.”
Or produce a good one. Upshop’s AI-powered software for food retailers does both, according to Sanders, by turning data into intelligence and intelligence into action. Say you’re a grocer and the deli counter’s bread delivery came in lighter than expected.
“If I’m only going to make a certain amount of sandwiches, which sandwiches should I make?” Sanders asks. “What’s the most likely thing to sell? What gives us the best profitability? Or what’s going to allow us to get the most coverage so we disappoint the fewest amount of guests?”
Or say instead that a bunch of milk in the dairy aisle will reach its expiration date in two days. Data tells you how many cartons are involved and what they’re worth to you. Intelligence tells you how much milk you would normally sell in two days and exactly how much you should lower your price by to sell everything at risk of expiring instead. An intelligent system of action, meanwhile, arms managers to put that price into effect automatically.
“You’re not just cutting the price in half or giving [milk] away for free,” Sanders says. “You’re making the best possible decision that you can to sell as much of it as you can while maintaining as much margin as you possibly can.”
Outcomes like that are more exciting to grocers than data, or AI for that matter. “They’re able to drive quite a bit more growth because they have the right products at the right time on the shelf,” Sanders says.
Software vendors and MSPs can learn a few things from Upshop. The company offers an industry-specific SaaS solution, for example, at a time when vertical specificity is one of the best forms of SaaSpocalypse insurance available, and it has more than just large volumes of data. It has large volumes of targeted, contextual data with a lot of retail-specific scaffolding around it.
“We’re allowing that larger data set to drive smarter decisions and smarter outcomes as a result,” Sanders says.
Which points to the biggest moral of Upshop’s story, especially for managed service providers remaking themselves as managed outcome providers: AI client conversations should more or less always center on increased sales, decreased waste, stronger margins, or something else tied to making more or spending less rather than AI itself.
Data makes AI work. Outcomes are what businesses buy.
Over on Business of Tech
Host Dave Sobel is pondering a topic on my mind lately too. What happens when help desk techs are no longer graduating into engineers because AI has replaced all the help desk techs? Sobel provides two options:
Manufacture the engineer. That means deliberately holding back work the AI in your own stack could already close — real tickets, on real clients — and routing them to a person who needs to learn on them … Or buy the engineer. Which means competing on salary against vendors, against integrators, and against your own clients, who are all hiring the same person you are … Pay for seniority in margin now, or pay for it in salary later. One of those you can budget.
Also worth noting
GTIA has acquired 42-year-old MSP community the ASCII Group. More to come next week.
NinjaOne has added browser management to its Unified IT Operations Platform.
Addigy’s new Intelligence Suite is an AI layer within its Apple device management platform designed to make Apple expertise and execution available on demand.
MSP360’s Backup for Proxmox Community Edition is now generally available.
OpenAI’s vertical AI push pushes on. Last week it was financial services. This week it’s legal. Next week?
Mailprotector now has a partner success team tasked with helping MSPs navigate an evolving email security threat landscape more profitably.
Aurora MDR Connect, from Arctic Wolf, is an MSP-exclusive tier of the company’s MDR service designed for faster deployment and broader attack-surface visibility.
Stellar Cyber and ESET have formed a technology partnership integrating ESET Threat Intelligence with Stellar Cyber’s Open Threat Intelligence Platform.
Keeper Security and SailPoint are integrating to combine the latter’s identity governance and administration technology with the former’s Identity Security Platform.
IDrive’s Microsoft 365 Backup offering now includes Microsoft Entra ID backup.
Devicie, who you’ve met here before, has added AI-assisted application management to its management and automation solution for Microsoft Intune.
ThreatCaptain, who you’ve also met here before, is the newest addition to the North American line card at TD SYNNEX.
Actually, it’s a tie for newest addition between ThreatCaptain and Hammerhead AI.
Ramp is the newest addition to Ingram Micro’s North American line card, and also now available on Microsoft Marketplace.
84% of MSPs expect demand for CISO-level services to increase during the next 12 months, according to Sophos.
48% of security leaders said AI agents with excessive, compromised, or unintended access are their organization’s greatest threat, according to Exabeam. Just 28% cited external threat actors.
New research from GoTo suggests workers are taking the good with the bad on AI. The good: it saves them an average of 2.3 hours a day. The bad: 83% of them worry they’ll be blamed or fired if it makes a mistake.
Version 4.0 of MSPAlliance’s Unified Certification Standard for Cloud and Managed Service Providers adds AI governance requirements among other things.